
Government Phones Are Already Targets
2011 | Pegasus on State Department iPhones
Reuters reported that NSO Group's Pegasus spyware compromised the iPhones of at least nine State Department employees based in Uganda or working on Uganda-related matters.
Dec 2024 | Salt Typhoon reaches senior officials' phones
China-linked hackers breached nine U.S. telecom companies. The intrusion swept up unclassified communications from senior U.S. government officials' phones.
May 2025 | FBI warns of AI impersonation of senior officials
The FBI warned that since April 2025, attackers had sent texts and AI-generated voice messages claiming to be senior U.S. officials, aiming to take over personal accounts and reach the officials' contacts.
Mar 2026 | Coruna and DarkSword iPhone exploit kits spread
Two iPhone exploit kits, used by surveillance vendors and suspected nation-state actors, prompted Apple to ship security updates for devices as old as iOS 15.
Apr 2026 | DHS Inspector General flags intelligence office phones
A DHS OIG audit found that "76 percent of apps installed on I&A mobile devices pose security risks, are prohibited, or allow prohibited activities," and that devices used abroad weren't properly authorized and protected.
Federal EDR requirements apply to the endpoints that handle official business, and phones are among them.
Civilian agencies
Executive Order 14028: Improving the Nation's Cybersecurity (May 2021)
Section 7 directs a government-wide EDR initiative to support proactive detection, active cyber hunting, containment and remediation, and incident response across federal infrastructure.
OMB M-22-01 (October 2021)
OMB M-22-09 (January 2022)
NIST SP 800-124 Rev. 2 (May 2023)
Department of War (DoD)
DoD Zero Trust Capabilities and Activities
The device pillar calls for DoD Components to "procure and implement Endpoint Detection and Response (EDR) solution(s)." The framework's device activities name "user devices (phones, desktops, laptops)."
FY2025 NDAA, Section 1515 (P.L. 118-159)
FY2026 NDAA, Section 1511 (P.L. 119-60)
iVerify doesn't replace your compliance program. It gives your team detection, response, and reporting on the phones these requirements already cover.
How iVerify Protects Federal Agencies
iVerify is the only complete Mobile EDR platform. It covers government-furnished equipment (GFE) and personal devices on iOS and Android, and works with or without MDM.
From Detection to Forensics
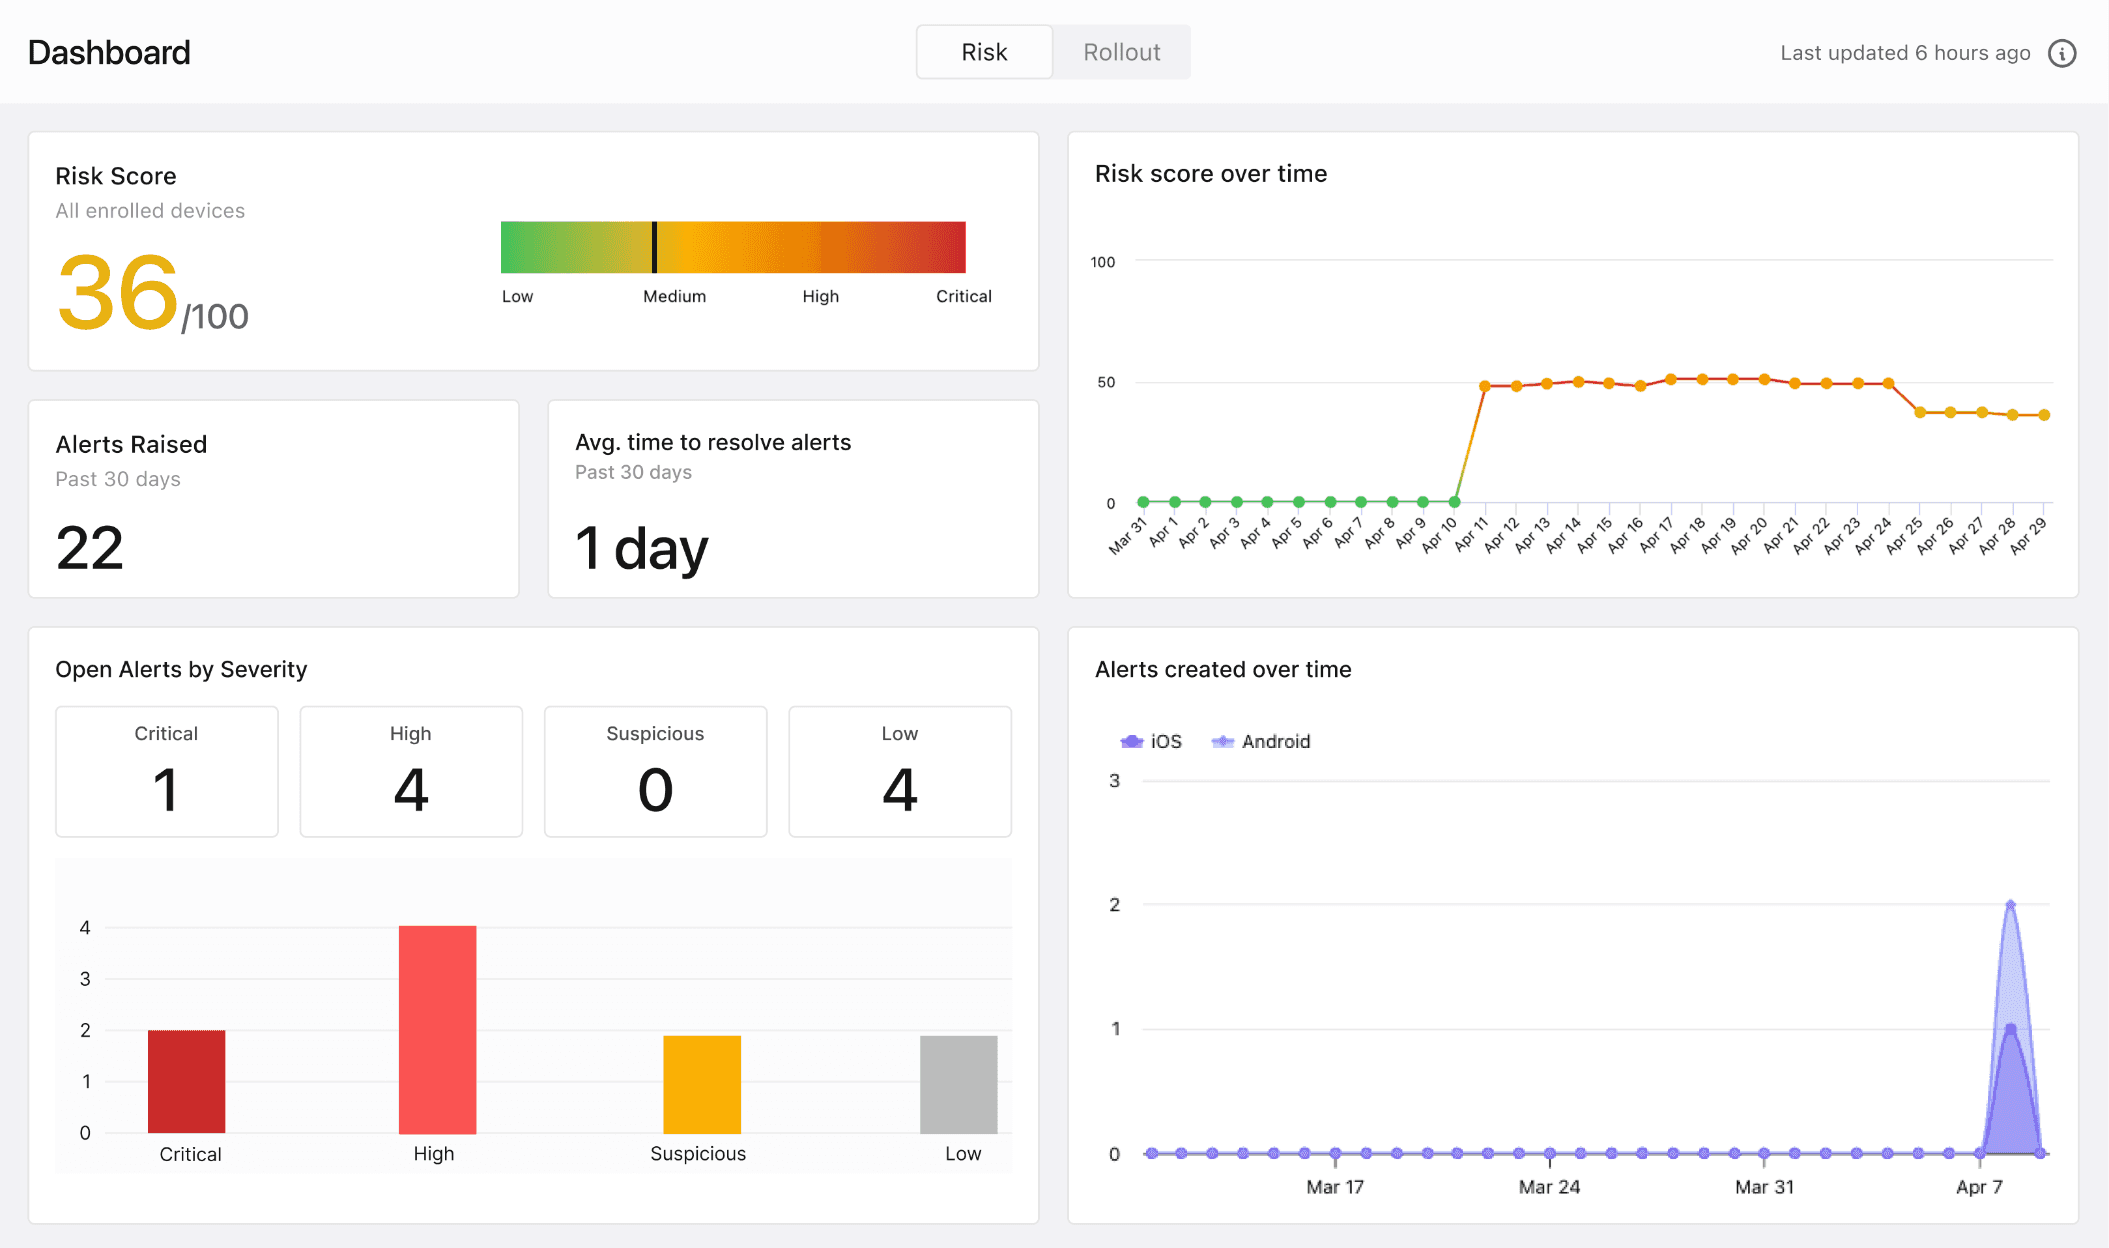
Detect (Seconds from infection)
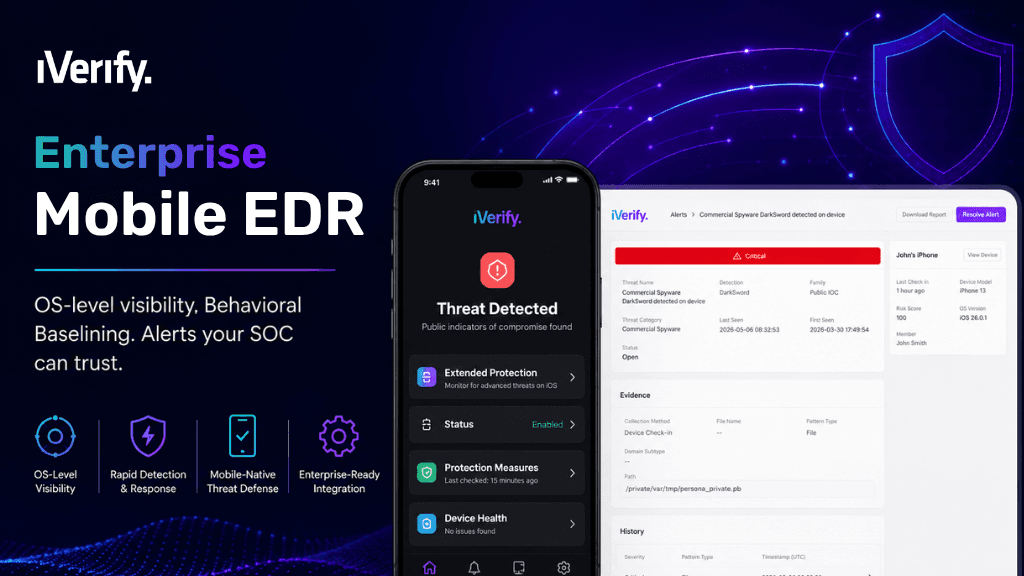
Always on, for every device. Kernel-adjacent telemetry and heuristic analysis flag spyware, zero-click exploitation, and device tampering in real time. Detection signals can feed conditional access through Okta, Microsoft Entra ID, and Omnissa Workspace ONE to protect agency data and reset credentials.
Triage (Minutes from infection)
When a detection fires, the iVerify Enterprise platform enables automatic requests for additional forensics, which the user can create and submit without leaving the app. iVerify's managed threat hunting team analyzes it and confirms whether it is a true or false positive, so your analysts get an answer instead of an unexplained alert.
IR Mode (Hours from infection)
When a compromise is confirmed, or when an attack is expected (for example, before an official travels to a high-risk region), IR Mode preserves forensic evidence on the device, captures malware samples, and helps your team understand the blast radius.
Full Forensic Extraction (Days later)
iVerify's forensics team runs a full file-system extraction, the step where malware samples are captured for analysis.
Related Resources for Government Security Teams


Federal Mobile Security Use Cases
Mobile Threat Visibility
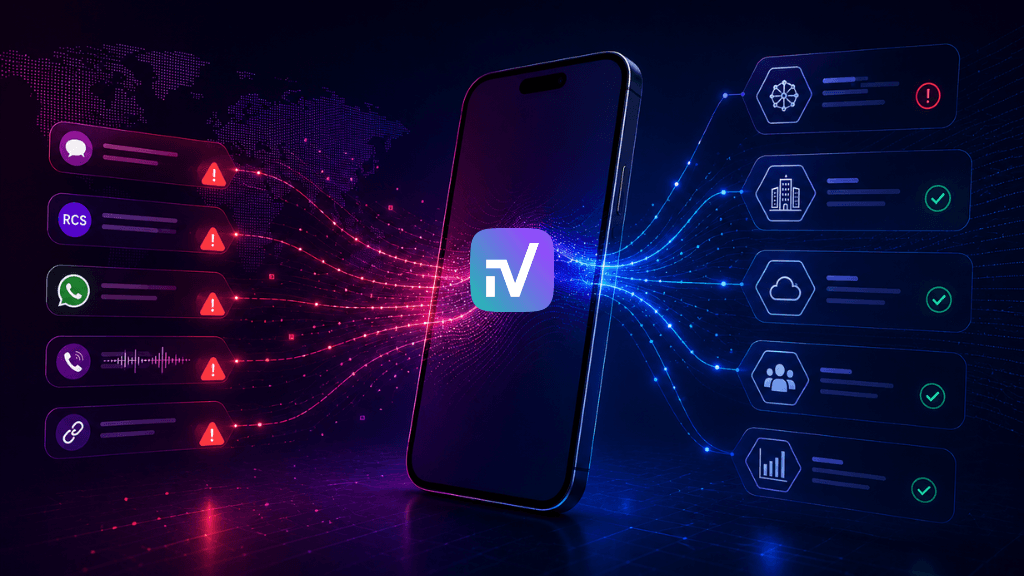
Phones are the endpoints most agency SOCs can't see. iVerify streams mobile telemetry into your existing SIEM, SOAR, XDR, and IAM tools through an open API and real-time webhooks, so phones show up in the same investigations as laptops and servers.
Active Mobile Compromise
MDM confirms that a device is enrolled and configured, but zero-click exploits, fileless malware, and spyware operate below that layer. iVerify runs continuous system-level analysis across every device to find active compromise, whatever MDM reports.
Malware and Spyware Detection
Mercenary spyware like Pegasus has already reached State Department iPhones, and exploit kits like Coruna and DarkSword are spreading well beyond nation-state hands. iVerify detects exploitation at the process and memory level, backed by the research team that tracks these kits, and alerts your team immediately.
AI-Accelerated Exploitation
AI has shortened the time from vulnerability to working exploit from months to days, and patch cycles can't keep up. iVerify detects active exploitation regardless of OS version or patch status, so a phone waiting on an update still has coverage.


BYOD and GFE Security
Deploy alongside MDM or MAM, or standalone. iVerify collects only the security telemetry needed to assess device integrity, with no PII collection and no monitoring of personal activity, matching the scope of NIST SP 800-124 Rev. 2, which covers both government-furnished and personal devices.
Credential Theft Protection
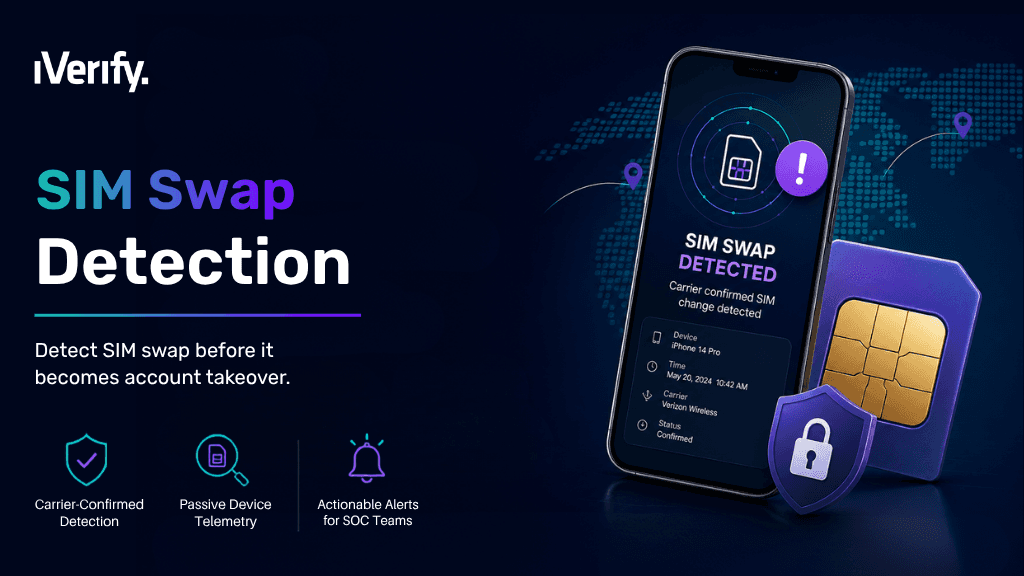
Officials are being impersonated with texts, AI-generated voice messages, and linkless lures across SMS, RCS, WhatsApp, and Signal. SmishGuard catches those attacks and blocks malicious links at the DNS level, and SIM swap detection alerts your team the moment a carrier-side transfer occurs, so you can act before it's used to intercept MFA codes. Messages are analyzed without identifying the device or recipient, so it works on personal phones too.
High-Risk Travel
Continuous monitoring before, during, and after official travel, with protection against malicious networks so personnel can keep using agency tools abroad. If a device may have been targeted, IR Mode preserves evidence before it reconnects to agency systems.
Mobile App Vetting
A DHS Inspector General audit found that 76 percent of apps on one intelligence office's phones posed security risks, were prohibited, or allowed prohibited activities. Through iVerify's integration with NowSecure, every app is scored for risk and monitored for behavior changes after approval, so a risky app doesn't stay on a device unnoticed.
Our researchers hunt the spyware and exploit kits aimed at high-value phones, and what they find ships as detections. They helped uncover DarkSword, tracked attackers fusing it with Coruna into DarkCoruna, and caught P7, a DarkSword variant no one had seen before, on a customer’s phone.
Bring Agency Phones Into Your EDR Program
Your laptops and servers already report to your SOC. iVerify adds the phones your personnel carry, government-issued and personal, with detection, triage, and forensic response built for iOS and Android.